Trust centre

Trust the tool before you trust the evidence.

SBOMFlow reads your source, firmware, and reviewer notes — so its own behaviour has to be checkable from outside. This page lists the properties you can verify without taking our word for them, then shows exactly how the v0.5.0 build was checked, including what that check did not establish. Everything here is a self-assessment with pointers to the evidence; none of it is a certification claim.

Verifiable from outside

Eight properties you can check without asking us.

01

Offline by default

Your code, SBOMs, and notes are read locally and written only to your output directory. Network access happens only on explicit, named opt-in paths, every one of them listed in the public docs — and there is no telemetry to switch off.

02

Deterministic

With inputs and run context pinned, the same inputs produce the same artifacts, byte for byte; timing measurements are excluded from determinism checks. Run it twice and compare the hashes yourself.

03

Real inputs, explicit gaps

Every result states its data source, and scanned files are hashed. What the engine could not read or could not determine is listed as a gap — never quietly dropped, never read as clean. Zero findings never means safe.

04

Human approvals

Observed is not reviewed. VEX status, evidence acceptance, and release decisions come only from recorded human review, and the release gate stays informational until you choose to enforce a policy.

05

Portable verification

Every output is a plain file you own; there is no database and no hidden state behind it. Bundles carry their hashes, and a recipient verifies them offline without installing SBOMFlow.

06

Open standards

SBOMs in CycloneDX 1.6 and SPDX 2.3; VEX in OpenVEX, CycloneDX, and CSAF 2.0; SARIF and CSV exports; an optional in-toto attestation over the bundle — readable by the tools and trackers you already run.

07

Secrets stay in the environment

Integration tokens are read only from environment variables, never from config or flags, and never written into any artifact. The opt-in network client is hardened against redirection to internal addresses and oversized replies.

08

Its own supply chain is thin

Zero required runtime dependencies, and SBOMFlow's own source goes through the same engine to produce its own SBOM. Today's v0.5.0 wheel is unsigned: its published SHA-256 is an integrity check, not a signature. Signed publication with build attestations is prepared for the first public release and is not yet in use.

Boundaries enforced in the engine, not just on this page:

  • Outputs are engineering evidence and gap assessments, never conformity claims.
  • It never files, transmits, or signs anything to a regulator — drafts stay unsigned and yours.
  • AI is never the source of truth; the core makes no required AI calls.
  • Observed is not reviewed — what the engine sees never becomes acceptance on its own.
  • Planned features are never presented as live — every capability carries its real status: available, experimental, in development, or planned.

How the v0.5.0 build you would receive was checked

Private tester build

v0.5.0 is a certified private tester build with no known release-blocking defects, subject to the documented restrictions. It is not published to PyPI and is not generally downloadable; approved testers receive the wheel through a controlled channel. Everything below is stated so you can check it rather than take it on trust — including the parts that were not established.

release/v0.5.0 verified offline
 tag      v0.5.0
 commit   36ac6478dd85aae9b35b99741ca201b80a249b9b
 wheel    sbomflow-0.5.0-py3-none-any.whl
 sha256   89a26452037dcaf523ff94132cc6c4ae92273f0c9aa82d8c15eab52342b54928
 rebuild  three byte-identical builds  (one machine, one interpreter, one OS)
 install  clean environment · zero network markers in the transcript
 package  385 of 385 archive entries inspected
 unsigned · no build-service attestation · not a conformity or security verdict
One immutable candidate — no result below is combined from a different source revision compare it yourself

Compare the SHA-256 against the file you receive. That comparison proves the bytes match the bytes the build produced — it is an integrity check, not a signature, and it does not establish who built them. We inspected every file inside the build we ship — all 385 — so “nothing found” means nothing was found, not that nothing was looked at.

What was established, and how:

  • Every mandatory release-certification lane ran and passed. None was skipped, and a skipped or not-gated lane would never have counted as a pass.
  • The build is deterministic here. Three byte-identical builds of the same source produced the same wheel digest — from independent producers, including a rebuild in a separate working tree that had no part in producing the release artifact.
  • A clean install works with no index. The wheel installs into a fresh environment with the package index and dependency resolution both switched off, and the installed command was then exercised end to end.
  • The install transcript contains no network markers. Five separate markers were swept for and none appeared — and each of the five was first shown to appear in a transcript of a networked install, so the zero is a measurement rather than a broken search.
  • Re-established by independent runs, not relayed. The release identity, the artifact digest, and the reproducibility of the build were each recomputed by a separate run rather than copied from the first one — on the same machine, by the same operator.

What was not established — read this part twice:

  • The build is unsigned. There is no cryptographic signature over the wheel and no publisher attestation.
  • There is no build-service attestation. The checks were run and recorded locally; nothing was attested by a hosted build service.
  • Reproducibility here is same-environment reproducibility. All three identical builds ran on one machine, one interpreter version and one operating system. Nothing was shown to reproduce byte-for-byte on a different platform or toolchain, and this must not be read as a cross-platform claim.
  • Optional trust layers were not exercised where their extra was absent. Where an optional component was not installed, no claim is made that the lane depending on it ran.
  • Native Windows is unverified. The verified platforms are Linux, macOS on Apple Silicon, and Windows via WSL.
  • “No known release-blocking defects” is not “error-free”. It means every defect found was closed or accepted with its restriction written down — not that none remains to be found.
  • None of this is a verdict about your product. It describes how this tool was built and checked. It is not a conformity, certification, safety or security conclusion about anything you ship.

Every number above has an examined count behind it, and every absence was calibrated against a case where it was shown to appear. A sweep that reports zero without ever having been seen to find one is not evidence, and none of the zeros here are that.
Tested for accuracy the way customers will actually use it

Engineering gate

Accuracy is measured adversarially, against what a real, messy manufacturer estate looks like: the synthetic manufacturer laboratory — ten synthetic connected-device businesses, full customer-shaped estates across Yocto, Zephyr, Buildroot, ESP-IDF, OpenWrt, ThreadX, and RPM — driven through the production CLI. A green run has to mean something, so:

  • Known-affected findings must be caught and known-clean components must stay clean — every run, against answer keys the engine never sees. A false positive fails the run as surely as a miss.
  • Any silent omission, false merge, missing provenance or overclaim fails — and so does any attempt to reach the network from the shipped command.
  • The laboratory is built to fail, and has — its checks are themselves shown to go red when the engine misbehaves, so a pass is proven, not assumed.

A recorded run of this laboratory is published, with its known gaps stated, as the accuracy scorecard. That recorded run was produced by 0.4.0; no run for 0.5.0 is published yet, and none is simulated. Separately, the Evidence Assurance Benchmark scores the installed product itself and publishes a number only when a qualified, independently re-verified receipt exists. Every name, domain, and file in the laboratory is fictional and labelled non-real.

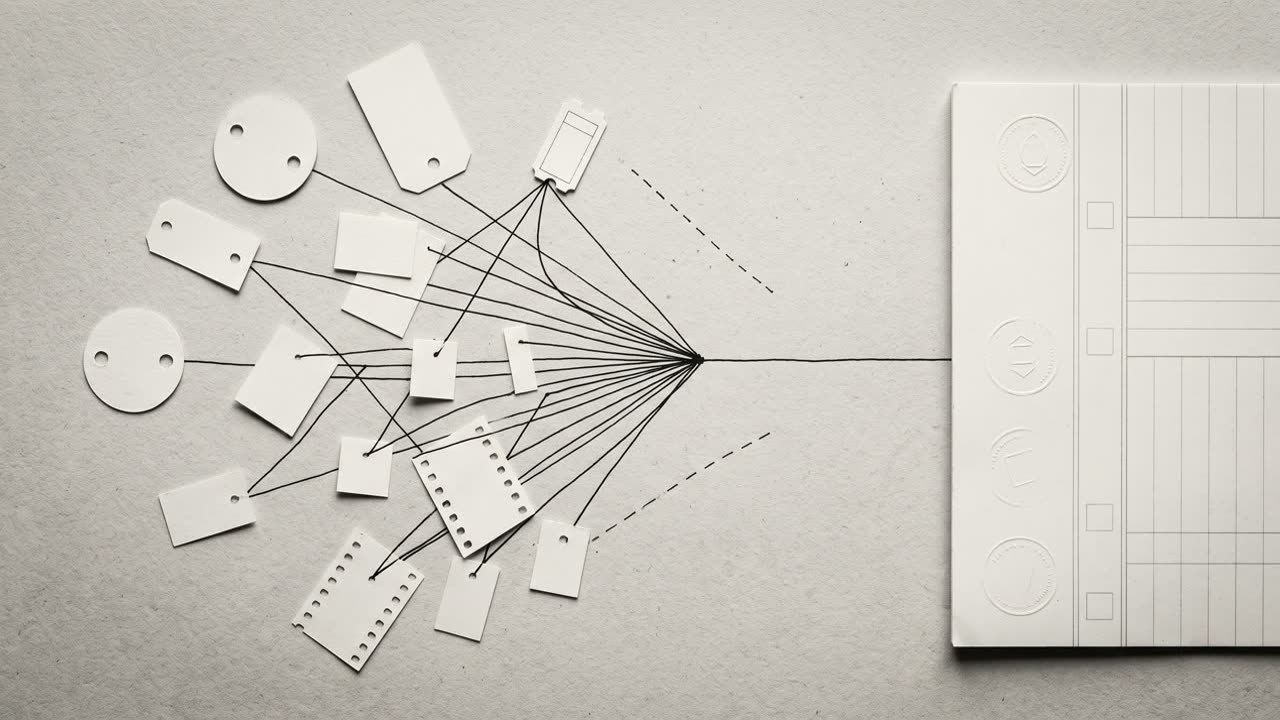
Illustrative brand image, synthetic: scattered paper evidence tokens connected by ink lines converging toward one ledger card, with two dashed lines deliberately left unresolved
Uncertainty stays visible: what can't be determined is surfaced, never quietly dropped — illustrative brand image · synthetic

A strong engineering gate — not a security certification or a proof of CRA conformity. It measures how accurately and safely the tool behaves under customer-shaped pressure. It makes no claim about your product.

What we publish, and what we don't

A deliberate three-layer disclosure model.

Trust does not require publishing the recipe — and nothing here relies on hiding one. Every security property above is observable from outside; what stays private is engineering detail, not a control. We publish what a buyer needs to evaluate the tool, document what a security review needs to verify it, and keep the implementation recipe out of the public layer.

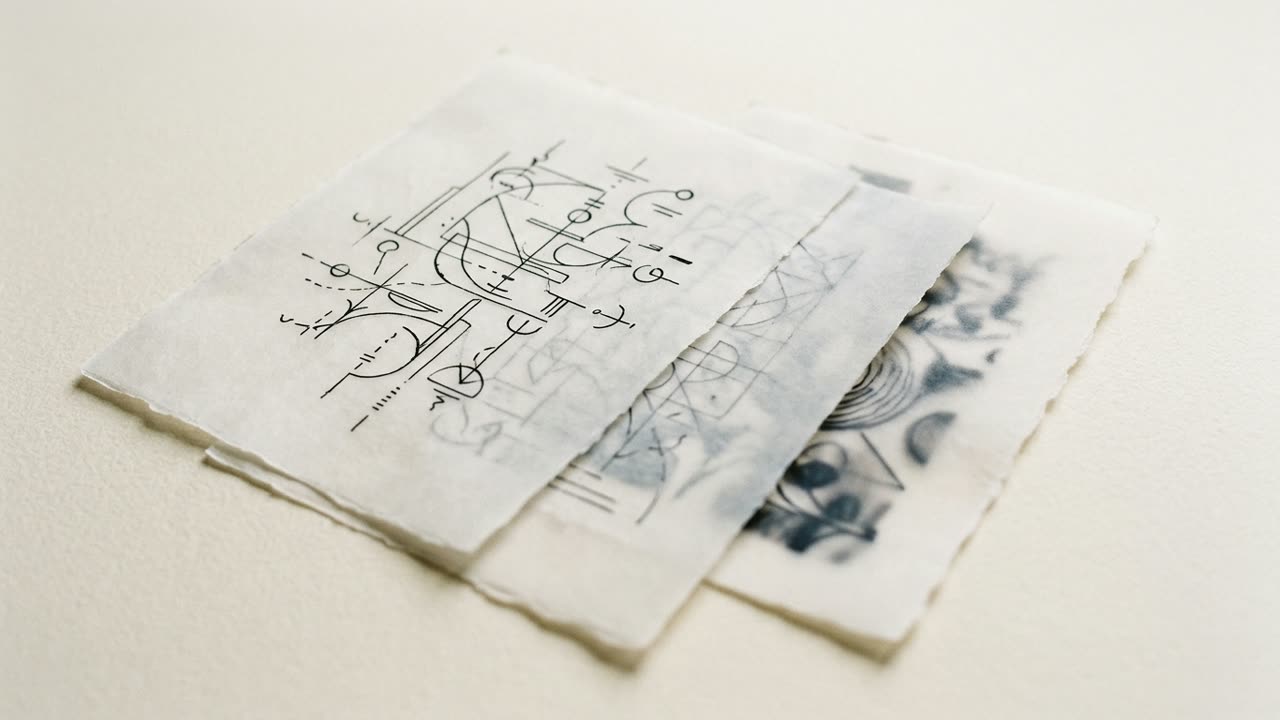
Illustrative brand image, synthetic: three translucent vellum sheets stacked with slight offsets — the top sheet crisp and fully readable, the middle softly veiled, the bottom mostly obscured
The model, literally: publish the top layer, document the middle for review, keep the bottom private — illustrative brand image · synthetic

Public marketing

Outcomes, supported inputs and outputs, standards, network posture, human decision boundaries, capability status, stated limitations. Every figure, digest, date and test-bound status label on these pages is drift-guarded against the code.

Public technical docs

Data flows, the network opt-in matrix, secret-handling policy, trust boundaries, validation methods, artifact verification instructions, residual risks — enough for a responsible evaluation without a call with us. Start at security & privacy and security-review readiness.

Private review

Detailed architecture, control implementation evidence, internal test reports, and non-public roadmap sequencing are available to qualified prospects and reviewers under an appropriate confidentiality process — ask.

Security reporting

Found something? Tell us directly.

Report suspected vulnerabilities in SBOMFlow to hello@sbomflow.com with "SECURITY" in the subject. We read every report, we won't pursue anyone acting in good faith, and we'll tell you what we find and when it's fixed.

FAQ

Straight answers, no overclaiming.

Does SBOMFlow make us CRA compliant?

No. SBOMFlow helps you collect, connect, and review cybersecurity evidence; it is not a certification and grants no regulatory approval. It produces engineering evidence and gap assessments to support CRA-oriented work, and qualified human review is always required.

Will it expose or leak our source, firmware, or IP?

It runs offline by default with no paid APIs, and your code is never sent to third-party services by default. It reaches the network only on named opt-ins — public vulnerability sources, and the tracker or notification integrations you explicitly apply. There is no telemetry to switch off. Outputs carry identifiers, counts, and hashes, and are designed never to include your secrets or source; an export preflight refuses secret-shaped content.

How do you know its results are accurate?

We measure it, adversarially — see the laboratory above, and the recorded 0.4.0 run on the accuracy scorecard; no 0.5.0 run is published yet. When something can’t be determined, it’s surfaced for human verification, never quietly dropped. The method is documented in Testing & trust — and it’s an engineering gate, not a claim of perfection.

How is this different from an SBOM generator or vulnerability scanner?

A generator answers “what’s in this build?” — SBOMFlow answers what happens next. It builds validated SBOMs from what it observes and also ingests the output of tools you already run (Trivy and Grype output, supplier SBOMs, and Syft when it is installed locally), then adds the layer those tools stop at: human review with recorded decisions, multi-role approvals, an explainable release gate, release-to-release drift, and a tamper-evident audit trail.

What do we need to run it?

Python 3.11+ and a real build tree — that’s it. Zero required runtime dependencies, no accounts, no server, nothing to send anywhere. It runs fully offline on a laptop or in locked-down CI (GitHub Actions, GitLab, Jenkins). Once you have the tester build, start with your first offline audit.

Can auditors or customers read the evidence without installing SBOMFlow?

Yes. Every output is a portable file: a static reviewer console and evidence bundle open in a browser with nothing installed, a no-install auditor package is built for exactly that handoff, and a redactable sharing pack covers importers and distributors. Hashes travel with the evidence, so a recipient can verify nothing was altered. See read an evidence bundle.

Is this an AI tool?

No — the evidence path is deterministic: results come from real builds, files, and human decisions, and the core makes no required AI calls. Separately, SBOMFlow is extending the release record to describe the AI inside your products — that AI Evidence capability is in development and clearly labelled. Sealed output from an external AI-assisted scanner can be imported as labelled, needs-review observations — never as SBOMFlow findings.

Does it file CRA reports for us?

No. SBOMFlow never files, transmits, submits, or signs anything, and never contacts a regulator or reporting platform. Any incident or declaration output is a clearly-marked UNSIGNED DRAFT for a person to complete and submit.

Does it replace our legal, security, or compliance review?

No. The engine observes; your people review and decide. It is designed to make expert review faster and better-evidenced — not to replace lawyers, consultants, auditors, or your own sign-off.

Is it production-ready?

The engine is deep and tested; the product experience is still being built. The offline engine is available today with a broad capability set behind thousands of deterministic tests. The current build, v0.5.0, is a certified private tester build with no known release-blocking defects, subject to the documented restrictions — which is a narrower statement than production-ready and is meant to be. Post-market and passport workflows are experimental previews, AI Evidence is in development, and shared review surfaces are planned. On the AI Evidence and use-case pages, status labels are enforced by tests against the capability record, so a planned feature can’t quietly call itself live.

Can we get the build, and how do we check it?

v0.5.0 is available to approved private testers. It is not on PyPI, there is no public download, and there is no installer to point you at. Approved testers receive the wheel through a controlled channel with its SHA-256, install it with the package index and dependency resolution switched off, and compare the digest against the value published above. That comparison proves the bytes are the ones the build produced; it is not a signature, and the build is unsigned. Ask at hello@sbomflow.com.

Something we haven’t answered? Ask us directly at hello@sbomflow.com — straight answers only. Commercial questions live on the design-partners page.

Don’t take this page on trust.

Everything above is written to be checked rather than believed. Start with the sample run — real v0.5.0 output on labelled synthetic data, read the way a reviewer would. Once you have the tester build, run an audit against a build you already know well and read what the run says it did not establish; your first offline audit walks through it.